
Firmware 9160342-S
2N Access Unit 2.0 RFID 13.56 MHz - Secured
2N 9160342-S este un dispozitiv de control acces, listat de producător la „Access control”.
Denumirea oficială a produsului este „2N Access Unit 2.0 RFID 13.56 MHz - Secured”.
Specificațiile detaliate pentru 9160342-S se preiau zilnic din catalogul 2N și apar aici imediat ce sunt publicate.
Ultima versiune de firmware publicată de 2N pentru 9160342-S este V2.50.2, din 02.10.2026. Mai jos găsești link-ul oficial de descărcare, notele de versiune și versiunile anterioare.
Firmware-ul se încarcă de obicei din interfața web a aparatului sau din software-ul de administrare al producătorului.
Firmware actual
| Versiune | Data | Regiune | Descărcare și note |
|---|---|---|---|
| V2.50.2Firmware 2.50.2 - 2N Access Unit | 02.10.2026 | Global | 5 MB Note de versiuneSHA-256: a6d83a81aa94208b4eafb8f50c0e1d2ba4568514342d147817b0da7971e093d5 Fișier: firmware_2_50_2_2n_access_unit.zip 2N OS version 2.50.2 for 2N IP Access Control Systems includes the following changes New Functions and Improvements Added support for new Wiegand module hardware revision. Essential Corrections Important bug fixes. 2N OS version 2.50.1 for 2N IP Access Control Systems includes the following changes Essential Corrections Fixed an issue with 2N Electronic Locks that limited the device directory to 2000 users. Fixed an issue where the ProfileStateChanged block in Automation functions caused an error after reboot. Fixed an issue where Access Unit 1.0 was unable to boot for an extended period after power loss. Updated several internal libraries. Important bug fixes. 2N OS version 2.50.0 for 2N IP Access Control Systems includes the following changes Precautions to be taken during update to FW version 2.50.x For security reasons, network settings can no longer be modified using 2N Network Scanner. All 2N OS devices (except those on the original platform: IP Vario, IP Force, IP Safety, IP Solo, IP/LTE Verso, IP Base, IP Uni, IP Audio Kit, IP Video Kit, Access Unit, SIP Speaker) can no longer be downgraded below version 2.47.0 after updating. Devices no longer accept certificates signed with 1024-bit RSA keys. These certificates are removed during the update and must be replaced with certificates using at least 2048-bit RSA or ECC keys. Services relying on weaker certificates will stop functioning, and a warning will appear next to the certificate selection parameter in the web interface. In EAP-TLS mode, 802.1x no longer supports RADIUS certificates containing the `id-kp-clientAuth` Extended Key Usage. If such certificates are used, they will be rejected after the update, resulting in the device being unable to authenticate and connect to the network. New Functions and Improvements Support for 2N Electronic Locks is now included as part of the standard firmware release. Essential Corrections Private keys are no longer exposed via `GET /api/mobilekey/config`. Updated several internal libraries. Web configuration pages for Automation features now load correctly even when the device is offline (without an active internet connection). Devices no longer crash when a user with a limited validity period presents their card, provided the associated RFID reader extension module has `Door` set to `Not used`. The `snmpget` function now works correctly on devices using SNMPv3. Fixed device crashes caused by specific malformed or non-standard ONVIF requests. Corrected an issue where video resolution could be incorrectly limited when selecting lower bitrate settings for the H.265 codec. Added a limited-range mode to the WaveKey opening algorithm to prevent unintended door openings from excessive distance. Other corrections and fixes. |
Versiuni anterioare
| Versiune | Data | Regiune | Descărcare și note |
|---|---|---|---|
| V2.50.1Firmware 2.50.1 - 2N Access Unit | 02.10.2026 | Global | 5 MB Note de versiuneSHA-256: a0c950c96b61b83e2eb69e2f29ef58dcadeb5d3560b8225f4d0820be92a26ef8 Fișier: firmware_2_50_1_2n_access_unit.zip 2N OS version 2.50.1 for 2N IP Access Control Systems includes the following changes Essential Corrections Fixed an issue with 2N Electronic Locks that limited the device directory to 2000 users. Fixed an issue where the ProfileStateChanged block in Automation functions caused an error after reboot. Fixed an issue where Access Unit 1.0 was unable to boot for an extended period after power loss. Updated several internal libraries. Important bug fixes. 2N OS version 2.50.0 for 2N IP Access Control Systems includes the following changes Precautions to be taken during update to FW version 2.50.x For security reasons, network settings can no longer be modified using 2N Network Scanner. All 2N OS devices (except those on the original platform: IP Vario, IP Force, IP Safety, IP Solo, IP/LTE Verso, IP Base, IP Uni, IP Audio Kit, IP Video Kit, Access Unit, SIP Speaker) can no longer be downgraded below version 2.47.0 after updating. Devices no longer accept certificates signed with 1024-bit RSA keys. These certificates are removed during the update and must be replaced with certificates using at least 2048-bit RSA or ECC keys. Services relying on weaker certificates will stop functioning, and a warning will appear next to the certificate selection parameter in the web interface. In EAP-TLS mode, 802.1x no longer supports RADIUS certificates containing the `id-kp-clientAuth` Extended Key Usage. If such certificates are used, they will be rejected after the update, resulting in the device being unable to authenticate and connect to the network. New Functions and Improvements Support for 2N Electronic Locks is now included as part of the standard firmware release. Essential Corrections Private keys are no longer exposed via `GET /api/mobilekey/config`. Updated several internal libraries. Web configuration pages for Automation features now load correctly even when the device is offline (without an active internet connection). Devices no longer crash when a user with a limited validity period presents their card, provided the associated RFID reader extension module has `Door` set to `Not used`. The `snmpget` function now works correctly on devices using SNMPv3. Fixed device crashes caused by specific malformed or non-standard ONVIF requests. Corrected an issue where video resolution could be incorrectly limited when selecting lower bitrate settings for the H.265 codec. Added a limited-range mode to the WaveKey opening algorithm to prevent unintended door openings from excessive distance. Other corrections and fixes. |
| V2.50.0Firmware 2.50.0 - 2N Access Unit | 02.10.2026 | Global | 5 MB Note de versiuneSHA-256: 2ceb66a096f64f11a9e75b04030428149d1415534597d6f6b38b76a10ef9969a Fișier: firmware_2_50_0_2n_access_unit.zip 2N OS version 2.50.0 for 2N IP Access Control Systems includes the following changes Precautions to be taken during update to FW version 2.50.x Devices no longer emit audible beeps during boot or network state changes by default. If required, this behavior can be enabled under `Hardware > Audio > Startup and Network States Signalization`. For security reasons, network settings can no longer be modified using 2N Network Scanner. All 2N OS devices (except those on the original platform: IP Vario, IP Force, IP Safety, IP Solo, IP/LTE Verso, IP Base, IP Uni, IP Audio Kit, IP Video Kit, Access Unit, SIP Speaker) can no longer be downgraded below version 2.47.0 after updating. Devices no longer accept certificates signed with 1024-bit RSA keys. These certificates are removed during the update and must be replaced with certificates using at least 2048-bit RSA or ECC keys. Services relying on weaker certificates will stop functioning, and a warning will appear next to the certificate selection parameter in the web interface. In EAP-TLS mode, 802.1x no longer supports RADIUS certificates containing the `id-kp-clientAuth` Extended Key Usage. If such certificates are used, they will be rejected after the update, resulting in the device being unable to authenticate and connect to the network. New Functions and Improvements Support for 2N Electronic Locks is now included as part of the standard firmware release. Essential Corrections Private keys are no longer exposed via `GET /api/mobilekey/config`. Updated several internal libraries. Web configuration pages for Automation features now load correctly even when the device is offline (without an active internet connection). Devices no longer crash when a user with a limited validity period presents their card, provided the associated RFID reader extension module has `Door` set to `Not used`. The `snmpget` function now works correctly on devices using SNMPv3. Fixed device crashes caused by specific malformed or non-standard ONVIF requests. Corrected an issue where video resolution could be incorrectly limited when selecting lower bitrate settings for the H.265 codec. Added a limited-range mode to the WaveKey opening algorithm to prevent unintended door openings from excessive distance. Other corrections and fixes. |
| V2.49.1.80Firmware 2.49.1.80 - 2N Access Unit 2.0 - 2N Fortis support · Etichetă regiune: Fortis | 02.10.2026 | Global | 19 MB Note de versiuneSHA-256: a3bcc920381b81ff777e70527e52c6046840270f8b71cbd6ea7f7f571c2a99b9 Fișier: firmware_2_49_1_80_2n_access_unit_2_0.zip 2N OS version 2.49.1 for 2N IP Access Control Systems includes the following changes Essential Corrections Updated an internal library containing critical vulnerabilities. Fixed a critical issue with DNS which caused the device to, e.g., become unable to re-register to a SIP server after its IP address changes. This also solved other DNS-related issues. Important bug fixes. 2N OS version 2.49.0 for 2N IP Access Control Systems includes the following changes Precautions to be taken during update to FW version 2.49.x Empty device names are no longer supported. Set the name via Services > Web Server > Device Name. If left blank, the device may fail to update. All 2N OS devices (except those on the original platform: IP Vario, IP Force, IP Safety, IP Solo, IP/LTE Verso, IP Base, IP Uni, IP Audio Kit, IP Video Kit, Access Unit, SIP Speaker) can no longer be downgraded below version 2.47.0 after updating. Devices no longer accept certificates signed with 1024-bit RSA keys. These certificates are removed during the update and must be replaced with certificates using at least 2048-bit RSA or ECC keys. Services relying on weaker certificates will stop functioning, and a warning will appear next to the certificate selection parameter in the web interface. In EAP-TLS mode, 802.1x no longer supports RADIUS certificates containing the `id-kp-clientAuth` Extended Key Usage. If such certificates are used, they will be rejected after the update, resulting in the device being unable to authenticate and connect to the network. New Functions and Improvements The administrator account now accepts "root" as a valid username as well. AXIS Camera Station integration has been significantly improved: The ACS tab in the web interface is now renamed to AXIS. AXIS Camera Station integration is now always enabled and accessible using the device's administrator account. After the initial login to the web interface, the "root" username can also be used for ACS access. An optional dedicated ACS account is now available. If ACS was previously enabled with both username and password configured, the dedicated account can still be used. If your dedicated ACS account used "admin" or "root" as the username and had the same password as the administrator account, it will be merged with the administrator account and you can continue using the same credentials. If your dedicated ACS account used "admin" or "root" but had a different password from the administrator account, it will be migrated to a temporary administrator account. You can continue using the same credentials, and the account will be merged with the administrator account after its password is updated. 2N IP Utility can now also be used to configure IP settings after the default password has been changed. Separate parameters are now available to independently enable and select modes for both License Pla |
| V2.49.1.75Firmware 2.49.1.75 - 2N Access Unit 2.0 | 02.10.2026 | Global | 19 MB Note de versiuneSHA-256: 4f4fc445877e819bfa1574637b09b8d45a7ee33d2cb9ca498f1fae3c88664288 Fișier: firmware_2_49_1_2n_access_unit_2_0.zip 2N OS version 2.49.1 for 2N IP Access Control Systems includes the following changes Essential Corrections Updated an internal library containing critical vulnerabilities. Fixed a critical issue with DNS which caused the device to, e.g., become unable to re-register to a SIP server after its IP address changes. This also solved other DNS-related issues. Important bug fixes. 2N OS version 2.49.0 for 2N IP Access Control Systems includes the following changes Precautions to be taken during update to FW version 2.49.x Empty device names are no longer supported. Set the name via Services > Web Server > Device Name. If left blank, the device may fail to update. All 2N OS devices (except those on the original platform: IP Vario, IP Force, IP Safety, IP Solo, IP/LTE Verso, IP Base, IP Uni, IP Audio Kit, IP Video Kit, Access Unit, SIP Speaker) can no longer be downgraded below version 2.47.0 after updating. Devices no longer accept certificates signed with 1024-bit RSA keys. These certificates are removed during the update and must be replaced with certificates using at least 2048-bit RSA or ECC keys. Services relying on weaker certificates will stop functioning, and a warning will appear next to the certificate selection parameter in the web interface. In EAP-TLS mode, 802.1x no longer supports RADIUS certificates containing the `id-kp-clientAuth` Extended Key Usage. If such certificates are used, they will be rejected after the update, resulting in the device being unable to authenticate and connect to the network. New Functions and Improvements The administrator account now accepts "root" as a valid username as well. AXIS Camera Station integration has been significantly improved: The ACS tab in the web interface is now renamed to AXIS. AXIS Camera Station integration is now always enabled and accessible using the device's administrator account. After the initial login to the web interface, the "root" username can also be used for ACS access. An optional dedicated ACS account is now available. If ACS was previously enabled with both username and password configured, the dedicated account can still be used. If your dedicated ACS account used "admin" or "root" as the username and had the same password as the administrator account, it will be merged with the administrator account and you can continue using the same credentials. If your dedicated ACS account used "admin" or "root" but had a different password from the administrator account, it will be migrated to a temporary administrator account. You can continue using the same credentials, and the account will be merged with the administrator account after its password is updated. 2N IP Utility can now also be used to configure IP settings after the default password has been changed. Separate parameters are now available to independently enable and select modes for both License Plate |
| V2.48.0Firmware 2.48.0 - 2N Access Unit - 2N Fortis support · Etichetă regiune: Fortis | 02.10.2026 | Global | 5 MB Note de versiuneSHA-256: 21a9330cb6044c8f84a8fd7e3353f9ecf64c610c1621b3a98d4e2f891434f4de Fișier: firmware_2_48_0_2n_access_unit.zip 2N OS version 2.48.0 for 2N IP Access Control Systems includes the following changes Precautions to be taken during update to FW version 2.48.x All 2N OS devices (except those on the original platform: IP Vario, IP Force, IP Safety, IP Solo, IP/LTE Verso, IP Base, IP Uni, IP Audio Kit, IP Video Kit, Access Unit, SIP Speaker) can no longer be downgraded below version 2.47.0 after updating. Devices no longer accept certificates signed with 1024-bit RSA keys. These certificates are removed during the update and must be replaced with certificates using at least 2048-bit RSA or ECC keys. Services relying on weaker certificates will stop functioning, and a warning will appear next to the certificate selection parameter in the web interface. In EAP-TLS mode, 802.1x no longer supports RADIUS certificates containing the `id-kp-clientAuth` Extended Key Usage. If such certificates are used, they will be rejected after the update, resulting in the device being unable to authenticate and connect to the network. New Functions and Improvements Support for 2N Electronic Locks with Secure Cards added. Devices can now generate Certificate Signing Requests (CSR) directly from the web interface under System > Certificates > CSR. Changing the web interface password now requires entering the current password. As a result, restoring a configuration will no longer change the password. Auto Provisioning can change the password only if the current one is still set to default. A firewall has been added to ARTPEC-based devices: IP Style, IP Verso 2.0, IP One, Access Unit QR, and IP Force 2.0. Essential Corrections Improved certificate handling. Prevented some certificates from reverting to factory defaults after a software factory reset (without selecting Network Settings), avoiding potential network disconnection. Removed certain unnecessary syslog messages. Improved formatting of exported Directory CSV files. The `UserAuthorized` Automation block now behaves correctly even for failed authorizations. DNS request lengths can now be up to 255 characters. RADIUS certificates are now validated properly in EAP-TLS/MSCHAPv2 scenarios. Commas in the Subject field of the `SendEmail` Automation block no longer cause the subject line to be truncated. Improved SMTP reliability. Enhanced handling of large-scale user directory operations. Important bug fixes. |
| V2.48.0Firmware 2.48.0 - 2N Access Unit 2.0 - 2N Fortis support · Etichetă regiune: Fortis | 02.10.2026 | Global | 17 MB Note de versiuneSHA-256: df4fbf85800c241dd227606f94c8560a81449fe4f04638ad3c732a1c7aeaf401 Fișier: firmware_2_48_0_2n_access_unit_2_0.zip 2N OS version 2.48.0 for 2N IP Access Control Systems includes the following changes Precautions to be taken during update to FW version 2.48.x All 2N OS devices (except those on the original platform: IP Vario, IP Force, IP Safety, IP Solo, IP/LTE Verso, IP Base, IP Uni, IP Audio Kit, IP Video Kit, Access Unit, SIP Speaker) can no longer be downgraded below version 2.47.0 after updating. Devices no longer accept certificates signed with 1024-bit RSA keys. These certificates are removed during the update and must be replaced with certificates using at least 2048-bit RSA or ECC keys. Services relying on weaker certificates will stop functioning, and a warning will appear next to the certificate selection parameter in the web interface. In EAP-TLS mode, 802.1x no longer supports RADIUS certificates containing the `id-kp-clientAuth` Extended Key Usage. If such certificates are used, they will be rejected after the update, resulting in the device being unable to authenticate and connect to the network. New Functions and Improvements Support for 2N Electronic Locks with Secure Cards added. Devices can now generate Certificate Signing Requests (CSR) directly from the web interface under System > Certificates > CSR. Changing the web interface password now requires entering the current password. As a result, restoring a configuration will no longer change the password. Auto Provisioning can change the password only if the current one is still set to default. A firewall has been added to ARTPEC-based devices: IP Style, IP Verso 2.0, IP One, Access Unit QR, and IP Force 2.0. Essential Corrections Improved certificate handling. Prevented some certificates from reverting to factory defaults after a software factory reset (without selecting Network Settings), avoiding potential network disconnection. Removed certain unnecessary syslog messages. Improved formatting of exported Directory CSV files. The `UserAuthorized` Automation block now behaves correctly even for failed authorizations. DNS request lengths can now be up to 255 characters. RADIUS certificates are now validated properly in EAP-TLS/MSCHAPv2 scenarios. Commas in the Subject field of the `SendEmail` Automation block no longer cause the subject line to be truncated. Improved SMTP reliability. Enhanced handling of large-scale user directory operations. Important bug fixes. |
Specificații 9160342-S
Garanție
| Length | 5 years (detailed terms: www.2n.com/warranty) |
|---|
Suitable for these products
| 2N Access Unit 2.0 |
Specificațiile sunt cele publicate de 2N, cu etichetele traduse în română (preluate la 05.11.2026). Ce nu am tradus a rămas în engleză.
Denumiri și variante: 2N Access Unit 2.0 RFID 13.56 MHz - Secured
Modele din aceeași serie
 Control acces2N Access UnitFirmware V2.50.2 · 02.10.2026
 Control acces2N Access Unit 2.0Firmware V3.3.1 · 31.08.2026
 Control acces2N Access Unit MFirmware V3.3.1 · 31.08.2026Control acces2N Access Unit QRFirmware V3.3.1 · 31.08.2026
 Control acces916031Firmware V3.3.1 · 31.08.2026
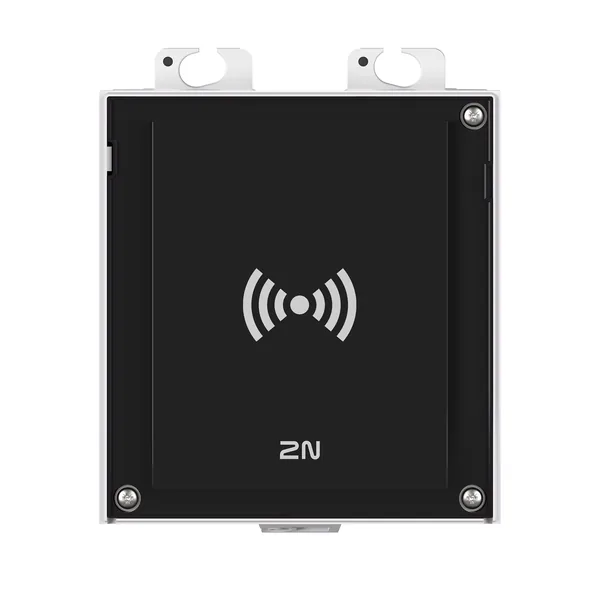 Control acces9160341Firmware V3.3.1 · 31.08.2026
 Control acces9160342Firmware V3.3.1 · 31.08.2026
 Control acces9160344Firmware V3.3.1 · 31.08.2026
 Control acces9160345Firmware V3.3.1 · 31.08.2026
 Control acces9160345-SFirmware V2.50.2 · 02.10.2026Control acces2N Access Unit 2 0 RFID Multifrequency SecuredFără firmware publicControl acces2N Access Unit 2 0 Touch KeypadFără firmware public