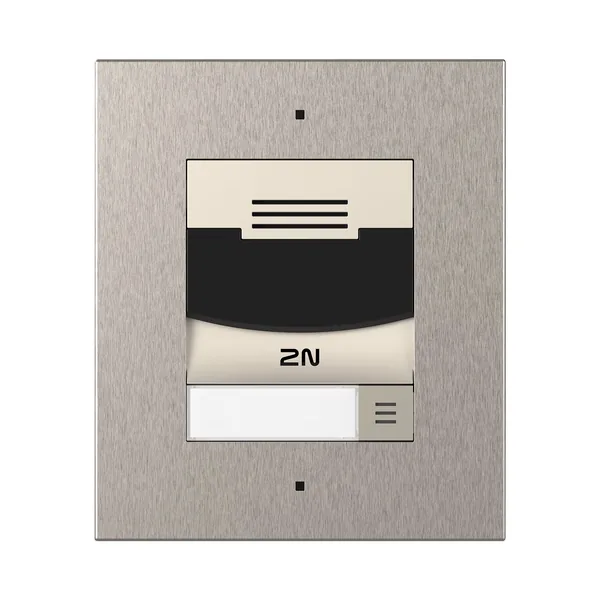
Firmware 9155301F
2N IP Solo without Camera – Flush Mounted
9155301F este un dispozitiv de videointerfon 2N din categoria „Intercoms”.
În catalogul 2N apare ca „2N IP Solo without Camera – Flush Mounted”.
Specificațiile detaliate pentru 9155301F se preiau zilnic din catalogul 2N și apar aici imediat ce sunt publicate.
La ultima verificare, cel mai nou firmware pentru 9155301F era V2.49.1.80 (18.11.2025). Pagina se actualizează zilnic din lista oficială 2N.
Aceeași versiune de firmware este publicată pentru 3 modele.
Firmware-ul se încarcă de obicei din interfața web a aparatului sau din software-ul de administrare al producătorului.
Firmware actual
| Versiune | Data | Regiune | Descărcare și note |
|---|---|---|---|
| V2.49.1.80Firmware 2.49.1.80 - 2N IP Verso, Solo, LTE Verso - 2N Fortis support · Etichetă regiune: Fortis · același fișier pentru 3 modele | 18.11.2025 | Global | 11 MB Note de versiuneSHA-256: ee2c8c7fb50d03c3ae30e8c2d50d8b4c7d5f678668b2c1fa013d03ead1070a06 Fișier: firmware_2_49_1_80_2n_ip_verso_solo_lte_verso.zip 2N OS version 2.49.1 for 2N Intercoms includes the following changes Essential Corrections Updated an internal library containing critical vulnerabilities. Fixed a critical issue with DNS which caused the device to, e.g., become unable to re-register to a SIP server after its IP address changes. This also solved other DNS-related issues. Important bug fixes. 2N OS version 2.49.0 for 2N Intercoms includes the following changes Precautions to be taken during update to FW version 2.49.x Empty device names are no longer supported. Set the name via Services > Web Server > Device Name. If left blank, the device may fail to update. All 2N OS devices (except those on the original platform: IP Vario, IP Force, IP Safety, IP Solo, IP/LTE Verso, IP Base, IP Uni, IP Audio Kit, IP Video Kit, Access Unit, SIP Speaker) can no longer be downgraded below version 2.47.0 after updating. Devices no longer accept certificates signed with 1024-bit RSA keys. These certificates are removed during the update and must be replaced with certificates using at least 2048-bit RSA or ECC keys. Services relying on weaker certificates will stop functioning, and a warning will appear next to the certificate selection parameter in the web interface. In EAP-TLS mode, 802.1x no longer supports RADIUS certificates containing the `id-kp-clientAuth` Extended Key Usage. If such certificates are used, they will be rejected after the update, resulting in the device being unable to authenticate and connect to the network. New Functions and Improvements The administrator account now accepts "root" as a valid username as well. AXIS Camera Station integration has been significantly improved: The ACS tab in the web interface is now renamed to AXIS. AXIS Camera Station integration is now always enabled and accessible using the device's administrator account. After the initial login to the web interface, the "root" username can also be used for ACS access. An optional dedicated ACS account is now available. If ACS was previously enabled with both username and password configured, the dedicated account can still be used. If your dedicated ACS account used "admin" or "root" as the username and had the same password as the administrator account, it will be merged with the administrator account and you can continue using the same credentials. If your dedicated ACS account used "admin" or "root" but had a different password from the administrator account, it will be migrated to a temporary administrator account. You can continue using the same credentials, and the account will be merged with the administrator account after its password is updated. 2N IP Utility can now also be used to configure IP settings after the default password has been changed. The `Enter PIN` button on the IP Style home screen is now blue to help distinguish it from call-related buttons. Separate p |
Versiuni anterioare
| Versiune | Data | Regiune | Descărcare și note |
|---|---|---|---|
| V2.49.1.75Firmware 2.49.1.75 - 2N IP Verso, Solo, LTE Verso · același fișier pentru 3 modele | 23.10.2025 | Global | 11 MB Note de versiuneSHA-256: e8650293f23e12a5d5514e5e256e01eea98999919c5c5985728f73b673e67536 Fișier: firmware_2_49_1_2n_ip_verso_solo_lte_verso.zip 2N OS version 2.49.1 for 2N Intercoms includes the following changes Essential Corrections Updated an internal library containing critical vulnerabilities. Fixed a critical issue with DNS which caused the device to, e.g., become unable to re-register to a SIP server after its IP address changes. This also solved other DNS-related issues. Important bug fixes. 2N OS version 2.49.0 for 2N Intercoms includes the following changes Precautions to be taken during update to FW version 2.49.x Empty device names are no longer supported. Set the name via Services > Web Server > Device Name. If left blank, the device may fail to update. All 2N OS devices (except those on the original platform: IP Vario, IP Force, IP Safety, IP Solo, IP/LTE Verso, IP Base, IP Uni, IP Audio Kit, IP Video Kit, Access Unit, SIP Speaker) can no longer be downgraded below version 2.47.0 after updating. Devices no longer accept certificates signed with 1024-bit RSA keys. These certificates are removed during the update and must be replaced with certificates using at least 2048-bit RSA or ECC keys. Services relying on weaker certificates will stop functioning, and a warning will appear next to the certificate selection parameter in the web interface. In EAP-TLS mode, 802.1x no longer supports RADIUS certificates containing the `id-kp-clientAuth` Extended Key Usage. If such certificates are used, they will be rejected after the update, resulting in the device being unable to authenticate and connect to the network. New Functions and Improvements The administrator account now accepts "root" as a valid username as well. AXIS Camera Station integration has been significantly improved: The ACS tab in the web interface is now renamed to AXIS. AXIS Camera Station integration is now always enabled and accessible using the device's administrator account. After the initial login to the web interface, the "root" username can also be used for ACS access. An optional dedicated ACS account is now available. If ACS was previously enabled with both username and password configured, the dedicated account can still be used. If your dedicated ACS account used "admin" or "root" as the username and had the same password as the administrator account, it will be merged with the administrator account and you can continue using the same credentials. If your dedicated ACS account used "admin" or "root" but had a different password from the administrator account, it will be migrated to a temporary administrator account. You can continue using the same credentials, and the account will be merged with the administrator account after its password is updated. 2N IP Utility can now also be used to configure IP settings after the default password has been changed. The `Enter PIN` button on the IP Style home screen is now blue to help distinguish it from call-related buttons. Separate para |
| V2.48.1Firmware 2.48.1 - 2N IP Verso, Solo, LTE Verso · același fișier pentru 3 modele | 11.08.2025 | Global | 11 MB Note de versiuneSHA-256: 338850783ad789db958791e61d36d86af6e0678c658b8e080c7dfb7a2547fe29 Fișier: firmware_2_48_1_2n_ip_verso_solo_lte_verso.zip 2N OS version 2.48.1 for 2N Intercoms includes the following changes Precautions to be taken during update to FW version 2.48.x All 2N OS devices (except those on the original platform: IP Vario, IP Force, IP Safety, IP Solo, IP/LTE Verso, IP Base, IP Uni, IP Audio Kit, IP Video Kit, Access Unit, SIP Speaker) can no longer be downgraded below version 2.47.0 after updating. Devices no longer accept certificates signed with 1024-bit RSA keys. These certificates are removed during the update and must be replaced with certificates using at least 2048-bit RSA or ECC keys. Services relying on weaker certificates will stop functioning, and a warning will appear next to the certificate selection parameter in the web interface. In EAP-TLS mode, 802.1x no longer supports RADIUS certificates containing the `id-kp-clientAuth` Extended Key Usage. If such certificates are used, they will be rejected after the update, resulting in the device being unable to authenticate and connect to the network. New Functions and Improvements IP Style now turns off the display backlight when idle to improve power efficiency. This setting can be adjusted via Hardware > Backlight > Backlight in Power Saving Mode. Devices can now generate Certificate Signing Requests (CSR) directly from the web interface under System > Certificates > CSR. All SIP accounts now support additional backup proxy and registrar servers. Accessibility features added to IP Style include Blind Assistance Mode and support for quick dial button modules. These can be configured under Calling > Dialing. The Bluetooth button on IP Style has been enlarged and centered in the navigation bar, which now shares a consistent design across both the standard and custom GUI interfaces. Changing the web interface password now requires entering the current password. As a result, restoring a configuration will no longer change the password. Auto Provisioning can change the password only if the current one is still set to default. A firewall has been added to ARTPEC-based devices: IP Style, IP Verso 2.0, IP One, Access Unit QR, and IP Force 2.0. Essential Corrections Improved certificate handling. The visitor message on IP Style is now shown only when access is granted during a call. Fixed occasional camera preview outages after reboot. Prevented some certificates from reverting to factory defaults after a software factory reset (without selecting Network Settings), avoiding potential network disconnection. Enhanced stability of IP Style when streaming and displaying multiple video feeds. SIP unregistration now works correctly with non-RFC-compliant User Agent Servers. Removed certain unnecessary syslog messages. Improved stability of the Custom GUI on IP Style. Improved formatting of exported Directory CSV files. `/api/camera/snapshot` now properly applies the `quality` parameter when supported. |
| V2.48.0Firmware 2.48.0 - 2N IP Verso, Solo, LTE Verso - 2N Fortis support · Etichetă regiune: Fortis · același fișier pentru 3 modele | 12.08.2025 | Global | 11 MB Note de versiuneSHA-256: 05354ba17f60dbcf64ecb7538e00bb99370191e4e0bdd353dba696ceb1faf399 Fișier: firmware_2_48_0_2n_ip_verso_solo_lte_verso.zip 2N OS version 2.48.0 for 2N IP Access Control Systems includes the following changes Precautions to be taken during update to FW version 2.48.x All 2N OS devices (except those on the original platform: IP Vario, IP Force, IP Safety, IP Solo, IP/LTE Verso, IP Base, IP Uni, IP Audio Kit, IP Video Kit, Access Unit, SIP Speaker) can no longer be downgraded below version 2.47.0 after updating. Devices no longer accept certificates signed with 1024-bit RSA keys. These certificates are removed during the update and must be replaced with certificates using at least 2048-bit RSA or ECC keys. Services relying on weaker certificates will stop functioning, and a warning will appear next to the certificate selection parameter in the web interface. In EAP-TLS mode, 802.1x no longer supports RADIUS certificates containing the `id-kp-clientAuth` Extended Key Usage. If such certificates are used, they will be rejected after the update, resulting in the device being unable to authenticate and connect to the network. New Functions and Improvements Support for 2N Electronic Locks with Secure Cards added. Devices can now generate Certificate Signing Requests (CSR) directly from the web interface under System > Certificates > CSR. Changing the web interface password now requires entering the current password. As a result, restoring a configuration will no longer change the password. Auto Provisioning can change the password only if the current one is still set to default. A firewall has been added to ARTPEC-based devices: IP Style, IP Verso 2.0, IP One, Access Unit QR, and IP Force 2.0. Essential Corrections Improved certificate handling. Prevented some certificates from reverting to factory defaults after a software factory reset (without selecting Network Settings), avoiding potential network disconnection. Removed certain unnecessary syslog messages. Improved formatting of exported Directory CSV files. The `UserAuthorized` Automation block now behaves correctly even for failed authorizations. DNS request lengths can now be up to 255 characters. RADIUS certificates are now validated properly in EAP-TLS/MSCHAPv2 scenarios. Commas in the Subject field of the `SendEmail` Automation block no longer cause the subject line to be truncated. Improved SMTP reliability. Enhanced handling of large-scale user directory operations. Important bug fixes. |
Specificații 9155301F
Garanție
| Length | 5 years (detailed terms: www.2n.com/warranty) |
|---|
Suitable for these products
| 2N IP Solo |
Specificațiile sunt cele publicate de 2N, cu etichetele traduse în română (preluate la 06.11.2026). Ce nu am tradus a rămas în engleză.
Documente oficiale
- Catalogue: 2N Catalogue for Planners 2026 (EN)
- Catalogue: 2N Product Catalogue (EN)
- Catalogue: Spare Parts Order No. (EN) – IP Intercoms
- Datasheet: Datasheet (EN) - 2N IP Solo
- Declaration of Conformity: Declaration of Conformity (EN) - 2N IP Solo
- Diagram: Diagram (EN) - 2N IP Solo
- Photos: 2N IP Solo photos
- Other: Nametags Print Template - 2N IP Verso, Solo
- Software: Software 3.0.9 - 2N Network Scanner
- Software: Software 1.1.7 - 2N IP Eye
- Security: 2N Hardening guide_EN.pdf
- Leaflets: 2N & CCURE Integration Overview Americas+APAC
- Leaflets: 2N & CCURE Integration Overview EMEA
- Leaflets: 2N Integration overview Leaflet
- Leaflets: Product Leaflet (EN) - 2N IP Solo
- Presentations: Presentation (EN) - 2N IP Intercoms
Denumiri și variante: 2N IP Solo without Camera – Flush Mounted
Modele din aceeași serie
 Videointerfon2N Audio KitFirmware V2.50.2 · 02.10.2026
 Videointerfon2N IP BaseFirmware V2.50.2 · 02.10.2026
 Videointerfon2N IP ForceFirmware V2.50.2 · 02.10.2026
 Videointerfon2N IP Force 2.0Firmware V3.3.1 · 31.08.2026
 Videointerfon2N IP OneFirmware V3.3.1 · 31.08.2026
 Videointerfon2N IP SafetyFirmware V2.50.2 · 02.10.2026
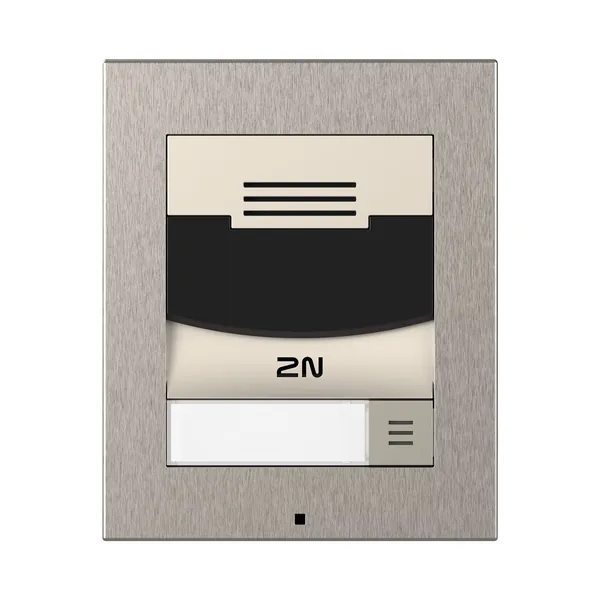 Videointerfon2N IP SoloFirmware V2.50.2 · 02.10.2026
 Videointerfon2N IP StyleFirmware V3.3.1 · 31.08.2026
 Videointerfon2N IP UniFirmware V2.50.2 · 02.10.2026
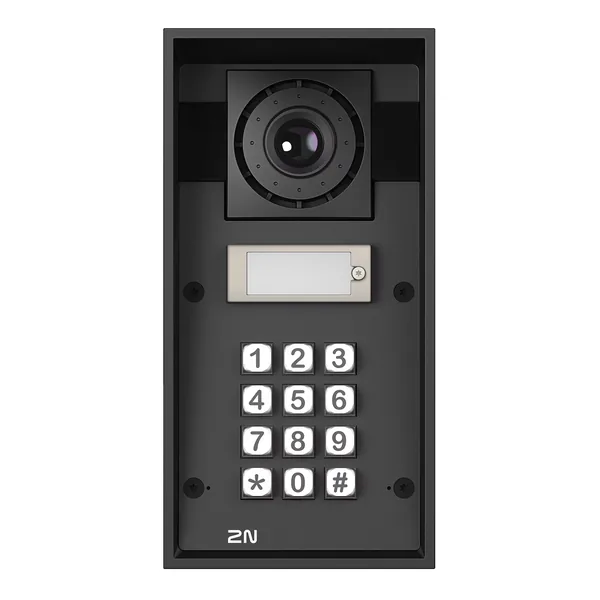 Videointerfon2N IP VarioFirmware V2.50.2 · 02.10.2026
 Videointerfon2N IP VersoFirmware V2.50.2 · 02.10.2026
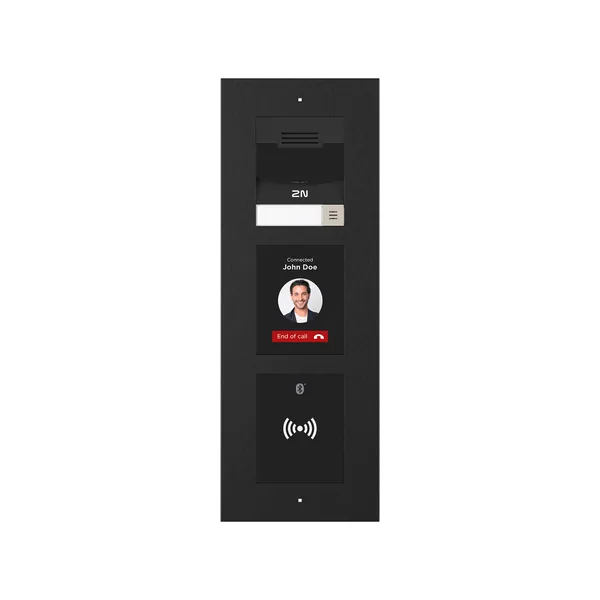 Videointerfon2N IP Verso 2.0Firmware V3.3.1 · 31.08.2026